StalkerZ DayZ DDoS Case Study: A Reported 643 Gbps Peak
How VYKIX adapted VxShield through StalkerZ's four DDoS rounds: a reported 643 Gbps peak, forged DayZ packets and changing payloads.

On this page
The Community at Stake
StalkerZ describes its DayZ world as a hardcore STALKER roleplay server on its About page. An outage keeps players from returning to that shared world.
After StalkerZ moved to VYKIX, we adapted VxShield through a campaign lasting more than 24 hours. The traffic changed across four rounds, reaching a reported peak of 643 Gbps. We updated packet and session checks as the attackers changed their payloads.
The original traffic charts and Harry’s Discord message accompany the sequence below. Harry identifies himself with StalkerZ and describes the customer’s experience of the move.
This is our reported historical campaign, not a statement of StalkerZ’s current hosting arrangement. Its undated public About page names Caliberservers as its host. The retained charts have clipped scales, and the player-session records are unavailable, so the exact peak and availability result remain unverified.
What Is Game-Aware DDoS Protection?
A packet’s port and header tell a filter where it is headed and what it resembles. To check whether it belongs to a player exchange, the filter needs to inspect its structure and session context. Doing that before it reaches DayZ reduces the work left to the game process.
Compare the checks enabled on the product you intend to use. OVHcloud documents a Layer 7 Game firewall on eligible products, with support varying by range. Ask which profile will run on your server and what traffic it validates.
The Previous Host
StalkerZ came to us after recurring attack-related problems. Harry discusses his dissatisfaction with the previous host in the message below. We do not have that deployment’s configuration or packet captures, so we cannot diagnose what failed there.
UDP Floods, A2S Queries and Forged Packets
VxShield had to handle volumetric flooding, A2S query abuse and packets imitating DayZ traffic in the same campaign. The network, browser listing and game sessions each needed the right checks.
Layer 1: UDP Volumetric Floods
Our account describes upstream mitigation of the UDP flood before it reached the DayZ host. The current VxShield service combines Global Secure Layer (GSL) upstream mitigation with additional filtering on VYKIX’s network; the charts do not show which layer produced them or which route the traffic took. We reported 643 Gbps at the campaign’s peak, rather than throughout its duration. We also had to account for packet rate: processing many packets creates pressure beyond the amount of bandwidth they consume.
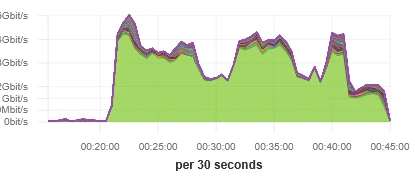 The chart is labelled “per 30 seconds”. The collector’s sampling and aggregation definition is unavailable. The left-axis values are clipped, so this view does not give an exact rate or a 30-second attack duration.
Layer 2: A2S Query Abuse
Steam uses A2S queries to obtain information for server listings. An A2S_INFO request has this standard format:
[FF FF FF FF] [54] [Source Engine Query\0] └─ Header └─ A2S_INFO type byteThis example illustrates the protocol; it is not a packet captured during the StalkerZ attack. A server can require the client to answer a challenge before it returns the requested information. Valve’s protocol announcement explains how the A2S_INFO challenge resists reflection using forged source addresses.
The current Valve query reference allows a challenge reply to any query. For A2S_INFO, append the four returned challenge bytes when resending the request. That exchange must pass the query filter; a successful browser reply still needs a separate game-join check.
Your server’s browser listing has its own query workload, even if game sessions are protected. The KarmaKrew case study explains how we handle that workload.
Layer 3: Packets Imitating DayZ Traffic
Some of the attack traffic resembled DayZ packets. A header check could recognize the format. That alone won’t tell you whether the packet belonged to a valid session.
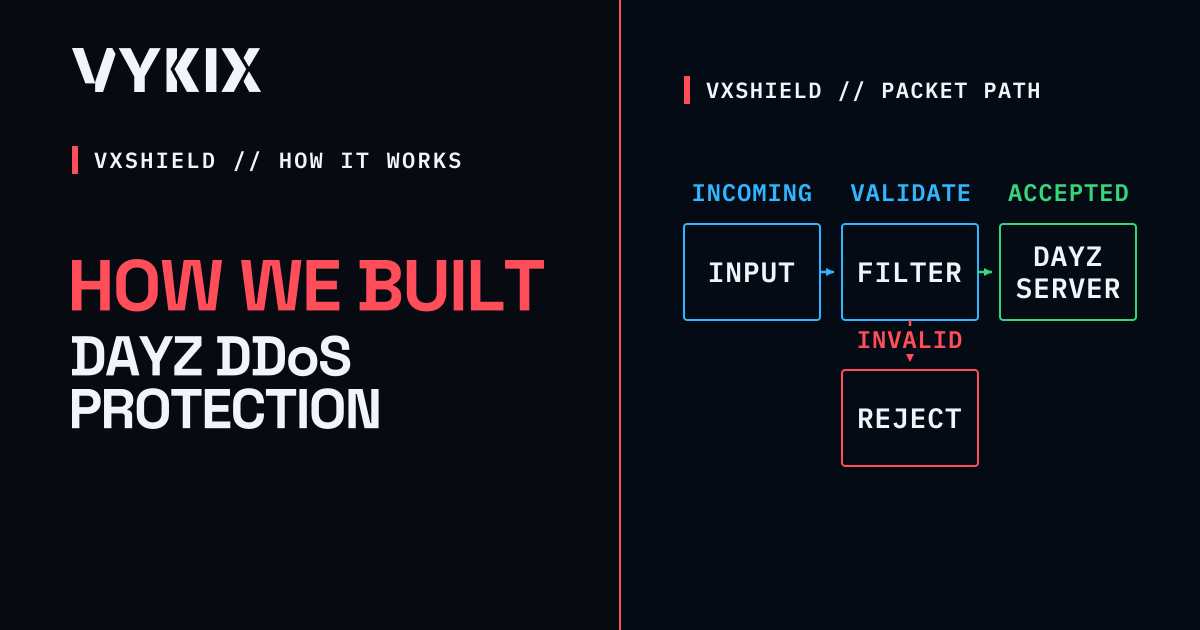
Our account describes a kernel-level DayZ profile checking packet structure, session context and rates before passing traffic to the game process. The forged payloads and deployed filter artifacts are unavailable, so we cannot demonstrate the exact validation rules used during this campaign.
See the DayZ DDoS protection guide for how the game, query and RCON rules work together.
The Migration and Changing Attack Rounds
StalkerZ faced these four rounds after moving to our DDoS protected DayZ hosting. Each round changed what the filters had to handle.
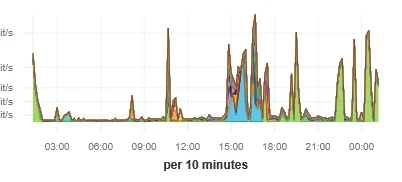 Campaign traffic with a “per 10 minutes” label and clipped vertical scale. The chart has no calendar date, timezone or markers assigning spikes to the four reported rounds.
Round 1: UDP flooding arrived with A2S query abuse, requiring the response to cover the network and the browser-query service.
Round 2: The traffic began to imitate DayZ packets. We had to assess payloads and session context alongside volume.
Round 3: A distributed push reached the reported 643 Gbps peak. We responded with a custom VxShield filter update.
Round 4: The payloads changed, prompting another update. The campaign ended after this round.
Each change meant reviewing the rules against the new traffic. A filter that handled one round needed checking again when the payload changed.
StalkerZ During the Campaign
We reported that StalkerZ remained available through the campaign. The independent uptime and player-session logs are no longer available to check that result.
Harry described the move and VYKIX’s protection in this Discord message:
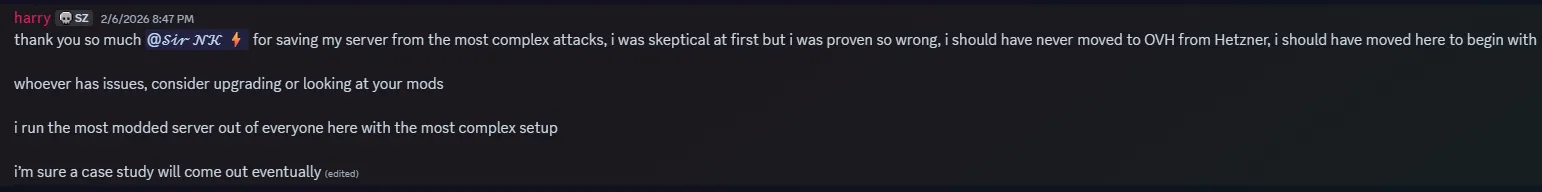 The retained message shows Harry with an SZ badge and the date “2/6/2026”. The date format leaves the calendar date unclear. The screenshot shows the message; it doesn’t verify who owns the account or whether StalkerZ currently hosts with VYKIX.
What to Check in a Game Protection Profile
StalkerZ’s campaign required us to review more than a bandwidth graph. These are the parts of VxShield’s response to check together when investigating a DayZ attack:
| Area | Evidence to request |
|---|---|
| Network limits | Bandwidth limits and packet-rate behavior |
| A2S queries | Supported requests, challenges and cache behavior |
| Game packets | The profile’s scope and its structure and session checks |
| Incident response | A log of rule changes and when they took effect |
| Player impact | Availability monitoring and game-session records |
Save the traffic and game records together. That gives you a way to compare the attack timeline with failed joins or interrupted sessions.
We cover the engineering work in how we built DayZ-specific DDoS mitigation. If you are troubleshooting a connection failure, the WinMTR report guide helps you collect network evidence before deciding what caused it.
Common Questions
How do I protect my DayZ server from DDoS attacks?
Confirm the protection enabled for your network, game traffic and A2S queries. Ask about bandwidth and packet-rate limits, packet validation and session checks. Find out which incident logs you and the provider can collect.
What is the difference between generic and game-specific DDoS protection?
Network controls check traffic volume and rate. A game profile can check packet structure and session behavior as well. Compare the profiles available on the hosting products you are considering.
Can DDoS protection stop protocol-level attacks on game servers?
Packet-structure and session checks can reject crafted traffic that a port or volume rule would accept. They work with network, query and rate controls, and need review as attack payloads change.
Why do DayZ servers get DDoS attacked?
We do not know who launched this campaign or why. Prepare a response plan around what you can check: incoming traffic, filter decisions and whether players can reach the server.
Review Your DayZ Protection
Check the game and query rules before you need them. Agree who collects logs, who can change filters and who will test player connections after an update.
VYKIX plans include VxShield. Confirm your DayZ profile and the configuration responsibilities that come with your chosen product. Check the live portal for the VAT-inclusive total and any unavoidable fees before paying.
Moving from another host? Eligible switchers receive best-effort migration and seven days added to the paid plan after VYKIX confirms the scope. Terms apply.
Move your DayZ server to VYKIX | Ask VYKIX on Discord
For more on query protection, read the KarmaKrew A2S case study. The 2.56 Tbps Ground Zero case study includes a detailed network report. Use the DayZ DDoS protection guide when configuring your server.
DayZ hosting for your community.
Review DayZ plans with VxShield DDoS protection and no added player-slot fee.