How Echoes of Chernobyl Beat a DayZ Packet Spoofing Attack
Our Echoes of Chernobyl migration account explains forged DayZ packets, session-aware checks and the limits of the original VxShield drop telemetry.
On this page
A packet can carry a familiar DayZ signature without belonging to a real player’s session. That was the filtering problem described in our STALKER: Echoes of Chernobyl migration account.
The RolePlay PvE community moved from OVH after attacks involving forged DayZ traffic, according to that account. For a persistent roleplay world, losing access can interrupt an event the group has spent time arranging. The operator needs to know whether traffic is reaching a valid game session, not just whether the port is open.
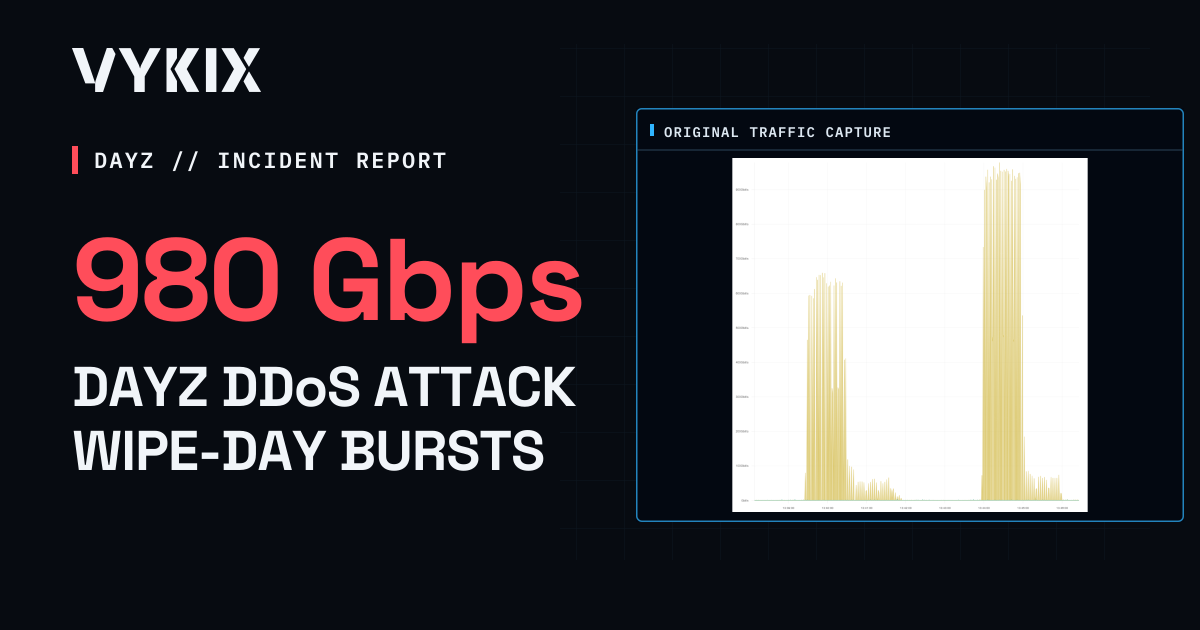
The original dashboards below show VxShield platform activity. We have no incident packet capture or bandwidth series here to reconstruct Echoes’ exact payloads, traffic volume or former hosting configuration.
What a DayZ Packet Spoofing Attack Is
In this account, spoofing means imitating the structure of DayZ game traffic. Source-IP spoofing is a separate property and would need its own evidence.
A filter working from port numbers and volume has limited context for that imitation. Structure, request rate and session state can help distinguish valid exchanges from traffic that only resembles them. Whether an attack exhausts the server also depends on its contents, rate and the controls in place.
Protocol imitation and a volumetric flood can occur in the same campaign, so keep both traffic classification and network load in view.
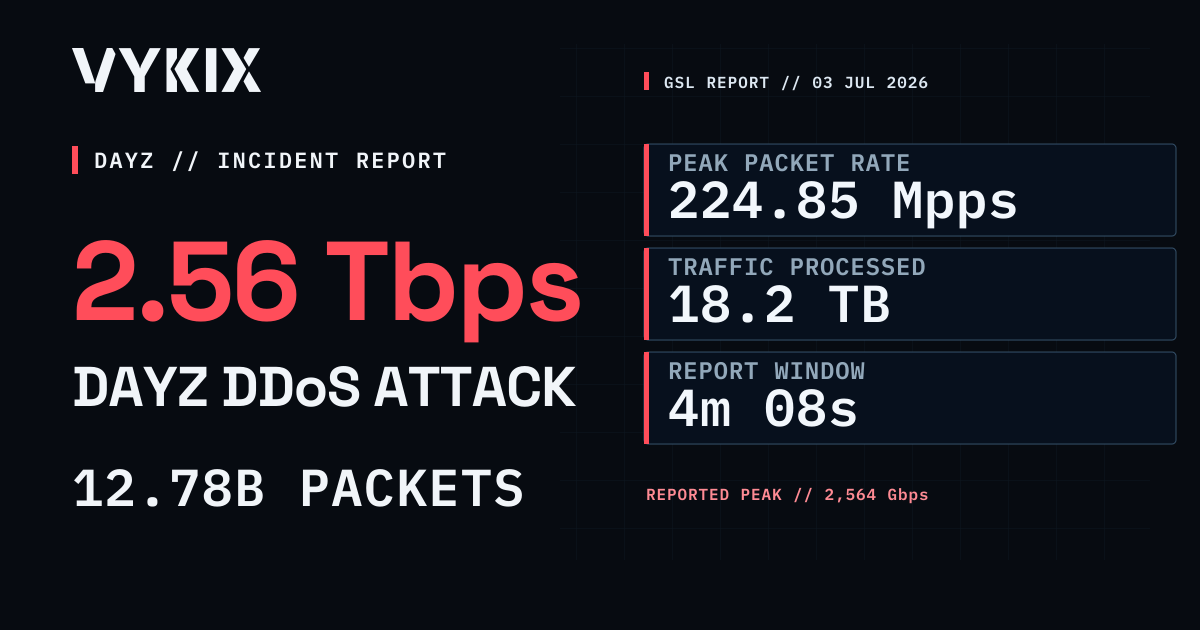
Our KarmaKrew A2S case study covers server-query abuse. The StalkerZ campaign account concerns a separate STALKER-themed community, while the 1.6 Tbps Rearmed retrospective covers our reported filter-development work. For a detailed network record, see the 2.56 Tbps Ground Zero report.
Why Generic DDoS Protection Lets Them Through
A volume threshold answers how much traffic is arriving. Application checks ask whether that traffic follows the exchanges the game expects. The profile and its configuration determine which checks are available.
OVHcloud documents a Layer 7 Game firewall for eligible Game servers, with profiles that vary by range and generation. Echoes’ former configuration is not retained, so the practical comparison is which checks are active on the deployment you are considering.
How DayZ-Aware Signature Validation Stops Forged Packets
Our DayZ filtering uses packet validation with session and rate controls. A signature is one input to that decision; it cannot prove intent or membership in a valid session by itself.
Our protection separates several jobs:
- Packet checks: bad-signature and size rules classify different rejected traffic.
- Session and rate controls: connection context accompanies packet structure.
- Query caching: supported DayZ A2S_INFO requests can receive cached replies, reducing listing work at the origin.
Dropping invalid traffic upstream keeps that work away from the game process. The dashboard below shows platform drop decisions, not traffic forwarded to Echoes’ server.
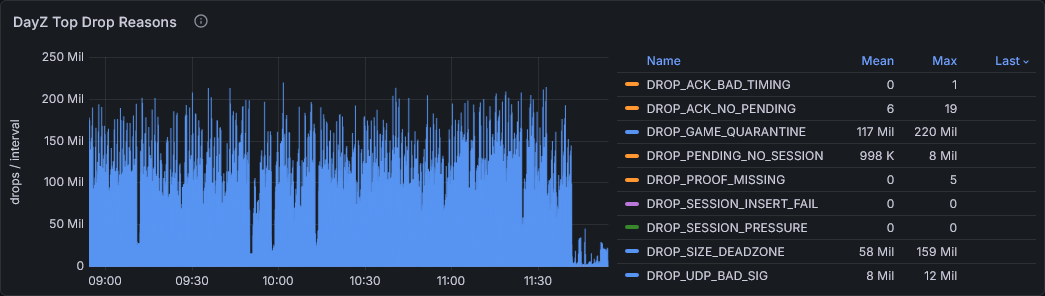 Platform drop telemetry. The displayed DROP_GAME_QUARANTINE maximum is 220 million drops per interval. DROP_UDP_BAD_SIG names a filter decision; it does not prove what a different provider would have passed or identify an Echoes-only count.
Our DayZ DDoS protection docs explain the controls and their configuration.
Inside the STALKER: Echoes of Chernobyl Migration
Moving a roleplay community means more than changing an address. Players still need to reach the world they have invested in, and the owner needs evidence that the fault has been understood.
Our account reports an improvement after Echoes moved, without matched uptime or session logs to quantify it. The response described here focused on judging traffic in context: a copied signature was not enough to treat a packet as part of a valid session.
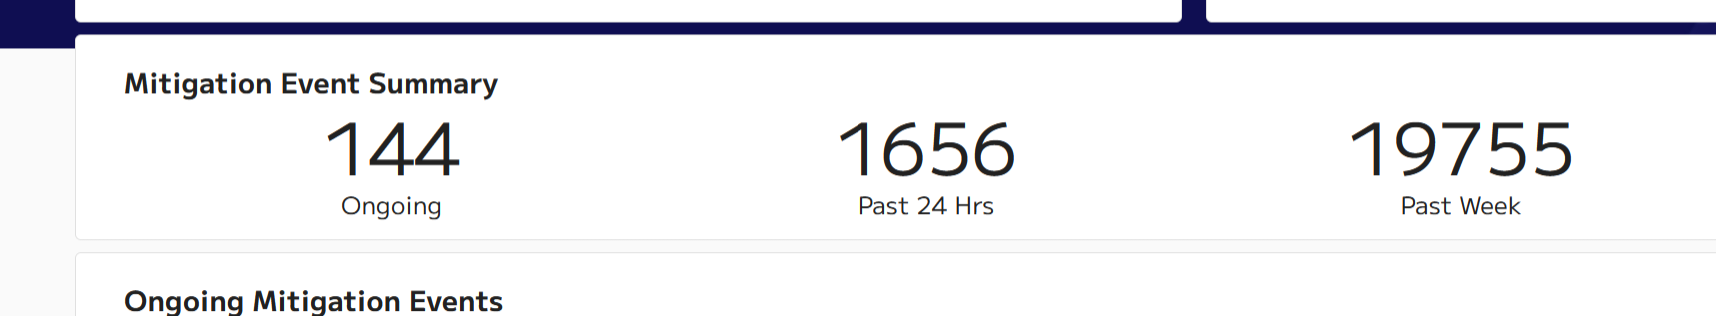 Platform event summary: 144 ongoing events, 1,656 in the past 24 hours and 19,755 in the past week at capture time. These are not counts attributed to Echoes of Chernobyl, and the date is not visible.
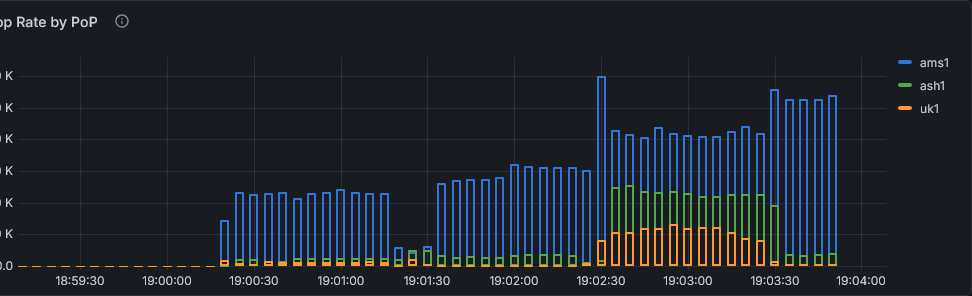 Original platform drop-rate view. The labels ams1, ash1 and uk1 identify series; the clipped scale and missing date limit quantitative interpretation and customer attribution.
For owners building a similar community, our DayZ PvE server guide covers the game setup. VYKIX DayZ hosting includes VxShield, alongside the configuration and workload tests the game itself still needs.
Common Questions
What is a DayZ packet spoofing attack?
Here, packet spoofing means forged traffic designed to resemble DayZ game packets. A copied signature does not authenticate a player. Packet structure, request rate and session context provide further checks.
Why can’t generic DDoS protection stop forged DayZ packets?
A volume-only rule has little application context. Game-aware structure and session checks can help, but products vary and a copied signature can pass a signature-only test.
Does OVH protect DayZ servers from DDoS attacks?
OVHcloud documents network mitigation and a Game firewall on eligible products. Check the supported profile and configuration for the server in question. This migration account does not establish the capabilities of every OVH product.
How do I protect my DayZ server from packet spoofing?
Ask for the active DayZ profile, packet and session controls, query protection, rate limits and incident records. VxShield is included with VYKIX plans; configuration and workload still affect the result.
If you are reviewing protection, bring the affected game and query paths and any incident records you have. VYKIX includes VxShield with its plans. Eligible switchers receive best-effort migration and seven days added to the paid plan after scope is confirmed; terms apply.
Game-aware DDoS protection for your server.
Run your game server with VxShield included. Ask about free migration and seven days free for eligible customers switching hosts. VYKIX confirms the scope, timing, and terms before the move.
Continue with